Understanding the Security Problem
The year is 1894. A meticulous French bureaucrat named Alphonse Bertillon is pioneering a revolutionary system. Using calipers, charts, and ink, he measures the head width, arm span, and middle finger length of every new prisoner. His method, bertillonage, is the world's first modern system of biometric identification. For the first time, a person’s identity is more than a name; it is a set of verifiable, supposedly unique data points. It’s a powerful idea: that who you are can be systematically cataloged, stored, and retrieved.
We have come a long way from calipers and inkwells. Yet, a century later, we find ourselves grappling with Bertillon's core problem on a planetary scale. Every click, every login, every new hire is an act of identity creation. Our digital selves are not measured in millimeters but in permissions, roles, and access rights, scattered across dozens, sometimes hundreds, of cloud applications. This sprawling digital archipelago is the landscape of modern work, and managing it has become one of the most silently critical challenges of our time.
This is the domain of Identity and Access Management, or IAM. In theory, it’s a beautiful concept: a single, authoritative source that dictates who gets access to what, and when. An employee joins, and the gates to their necessary tools swing open. They leave, and with a single click, those gates are sealed behind them. Clean. Efficient. Secure.
The reality, however, is a chaotic, hand-stitched patchwork.
Imagine a gifted architect named Elena. She joins a vibrant, growing tech firm. On her first day, IT manually creates her accounts for email, the design software, the project management tool, the cloud storage platform, and the company’s HR portal. Each one requires a slightly different username format, a unique set of permissions. When she’s promoted six months later, her access needs to be updated. Someone has to go into each of those five systems—and the three new ones her team adopted—and individually elevate her permissions. When she finally leaves for a new venture, a beleaguered IT administrator must hunt down every one of her digital ghosts and manually perform an exorcism. Did they miss one? It’s a question that keeps CISOs awake at night.
This is why most IAM strategies are quietly failing. They are failing not because the idea is wrong, but because the execution is fundamentally human, and therefore, fundamentally flawed. Manual provisioning is the digital equivalent of bertillonage—a well-intentioned but brittle, slow, and error-prone system buckling under the weight of modern complexity. It creates security gaps, wastes countless hours, and frustrates everyone from the new hire to the system administrator. We’ve built a federation of incredible cloud tools, but we’ve forgotten to build the bridges between them.
Enter SCIM.
If that acronym sounds dry and technical, it’s because it is. SCIM stands for System for Cross-domain Identity Management. But to dismiss it as jargon is to miss its quiet revolution. SCIM is not another application to manage; it’s a language. It’s the digital Esperanto that allows all these disparate cloud services to talk to each other about one thing: you.
Think of it like this. Before standardized shipping containers, loading a cargo ship was a nightmare of mismatched crates, barrels, and sacks. It was slow, inefficient, and prone to breakage. The standardized container changed global trade by creating a universal format. It didn’t matter if you were shipping Belgian chocolates or Japanese electronics; they all went into the same kind of box.
SCIM is the standardized container for human identity.
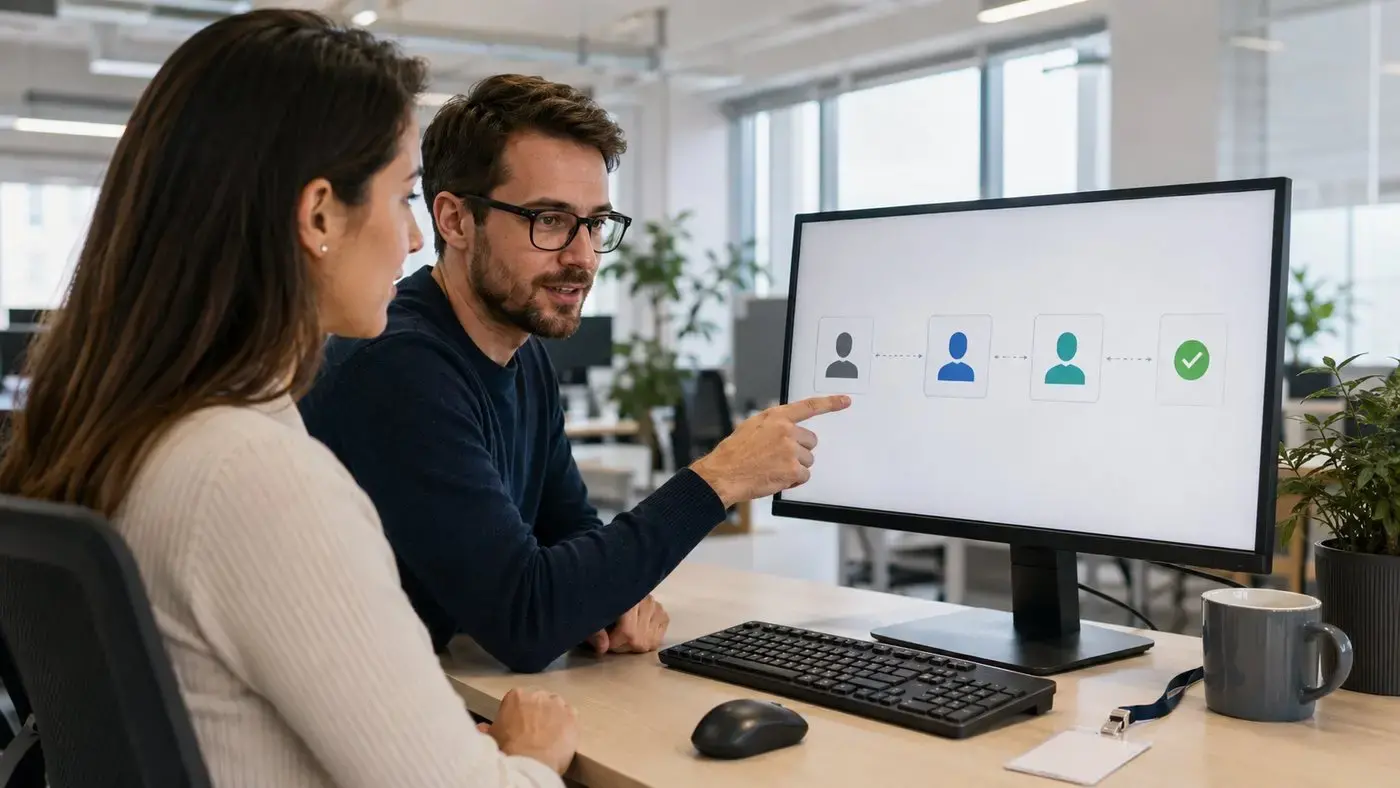
When a company adopts SCIM, it creates a universal protocol for identity information. When Elena the architect joins, the central identity provider (like Okta, Azure AD, or JumpCloud) doesn't just hold her credentials. It packages her identity—name, role, department, permissions—into a standardized SCIM "container." It then automatically ships this container to every application that speaks SCIM. The design software receives it and instantly creates her account with “Architect” permissions. The project management tool gets it and adds her to the “Skyscraper” project team. The process is instant, consistent, and automated.
When she gets promoted, the change is made once in the central system. SCIM broadcasts this update, and all connected applications adjust her permissions accordingly. And when she leaves? The central system sends out a single “delete” command. The SCIM protocol ensures that every door is not just locked, but that her identity is expunged from every system, a clean and complete digital departure.
The elegance of this system lies in its simplicity. It’s a promise whispered between machines: “When you tell me about a person, I will understand. I will create them, update them, and remove them without a human ever having to touch me.” This isn’t just about efficiency; it’s a profound shift in how we approach digital trust and security. By removing the fallible human hand from the process, we eliminate the vast majority of errors that lead to security breaches—the forgotten account, the overly generous permission, the "temporary" access that becomes permanent.
This is more than a technical fix. It’s a philosophical one. For too long, we have treated our digital identities as a series of isolated reflections in a fractured mirror. SCIM proposes something more whole: a single, authoritative source of digital self that can be projected, managed, and retracted with integrity. It restores a sense of coherent identity in a fragmented digital world.
Alphonse Bertillon believed he could create a permanent, infallible record of human identity. His system ultimately failed, replaced by the simpler, more scalable technology of fingerprinting. We stand at a similar inflection point. The manual, bespoke methods of managing digital identity are our bertillonage—clever for their time, but destined for the museum of legacy tech. The future is not about manually measuring each digital person. It is about creating a common language that allows their identity to flow, securely and seamlessly, wherever it needs to go. It’s about finally building the bridges between our islands.
What a Reliable SCIM Rollout Requires
Automation is only as trustworthy as the source information behind it. Before connecting applications, define which system owns employment status, department, manager, role, and other attributes that drive access. Standardize those values and decide how exceptions are approved. If the authoritative directory contains inconsistent departments or outdated managers, SCIM will distribute those mistakes quickly and consistently.
Start with a limited application and a small user group. Test new hires, transfers, leaves of absence, contractors, renamed users, and departures. Confirm not only that accounts are created, but that group membership and entitlements change correctly and that deactivation occurs within the required time. Preserve audit logs so teams can explain who changed an identity, when the update was sent, and how the receiving application responded.
SCIM also needs operational ownership. Someone must monitor failed provisioning events, reconcile accounts that were created outside the standard process, and review applications that support only part of the protocol. With clean source data, careful testing, and clear responsibility, SCIM becomes more than a connector. It becomes the dependable lifecycle layer that keeps identity policy aligned with the reality of the workforce.